OPERATIVE FILE / KOLKATA, INDIA / STATUS: ACTIVE

DEBJIT
Das

Cybersecurity researcher and ethical hacker building tools for offensive security research and defensive resilience — creator of ARMAGEDDON, DEMON PDF Crack Engine, PHOENIX OSINT Engine, GhostRoute C2 and WebRTC C2. Every engagement is authorized, documented, and disclosed responsibly.

9
Tools Deployed
2
Internships
13
Credentials Held
∞
Under Study
VERIFIED
ETHICAL &
AUTHORIZED
Scroll
01 — Identity

Subject Profile

Ref. DD—KOL—2026

I'm Debjit Das, a Cybersecurity Researcher and Ethical Hacker based in Kolkata, currently reading for a BSc in Cybersecurity at IAER Salt Lake.

My work spans both sides of the fence:  offensive security, red teaming, VAPT, bug bounty  — and defensive, forensic engineering. I build the tools I need for that research myself, from browser-security stress platforms to OSINT correlation engines and C2 simulation frameworks for red team training.

Creator of ARMAGEDDON, DEMON PDF Crack Engine, PHOENIX OSINT Engine, Project Nexus, GhostRoute C2 and WebRTC C2. Intern at THIRANEX and CFSS. Founder of CyberSec Cohort, a mentorship program for early-career security researchers. CTF competitor at Nullcon Berlin 2025.
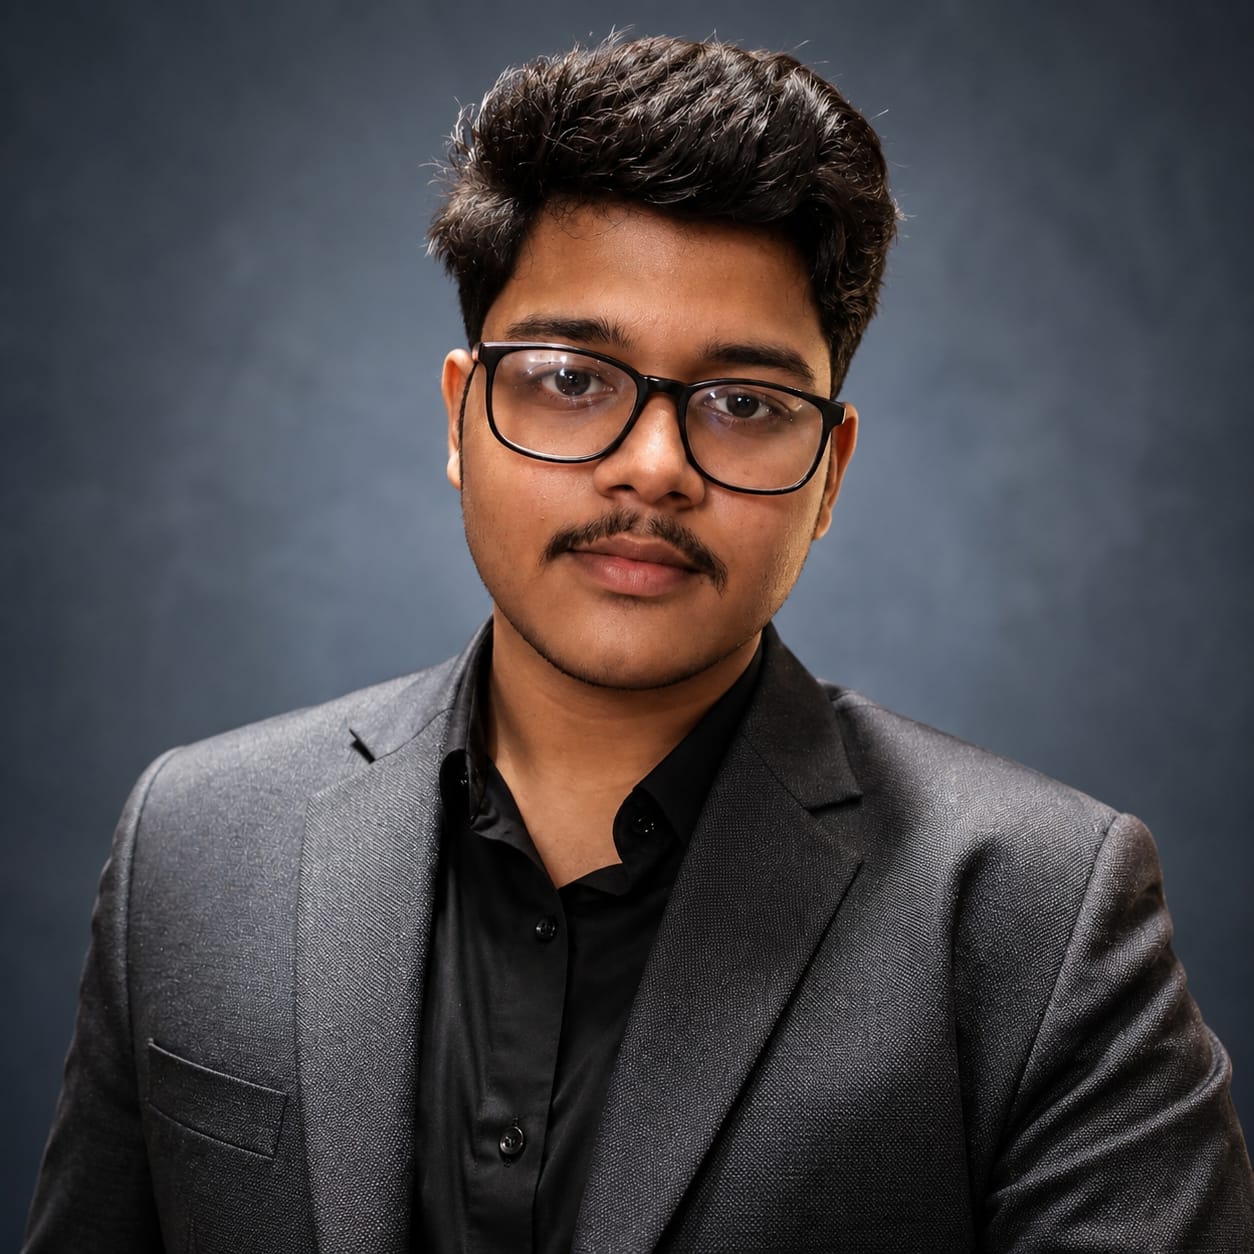
"Security is a process, not a product. Research ethically. Build responsibly. Defend relentlessly."
Debjit Das
DEBJIT DAS
ACTIVE — RESEARCHING
LOCATIONKolkata, West Bengal, IN
ROLECybersecurity Researcher
EDUBSc Cybersecurity — IAER Salt Lake
OSKali Linux / Arch
LANGEnglish · Hindi · Bengali
02 — Proficiency

Capability Matrix

Ref. DD—CAP—2026
Security Research
Browser Security Analysis92%
Cryptographic Security90%
Security Assessment (VAPT)88%
Red Team Simulation78%
Tools & Frameworks
Nmap / Masscan92%
Burp Suite Pro88%
Metasploit / BloodHound85%
Wireshark / Splunk82%
Ghidra74%
Development & Scripting
Python / Scikit-Learn88%
Bash / Shell85%
JavaScript / Node.js / React82%
C / C++68%
Signature Tooling
ARMAGEDDONDEMON PDF Crack PHOENIX OSINTProject Nexus GhostRoute C2WebRTC C2 WebGL 2.0 / WASMMITRE ATT&CK Django / ReactBug Bounty CTFEDR Analysis
03 — Chronology

Case Log

Ref. DD—LOG—2026
2026
Cybersecurity Intern — THIRANEX
Advanced cybersecurity operations, threat analysis, and security tool development.
2026
Cybersecurity Intern — CFSS
Vulnerability assessment, digital forensics, and cybersecurity frameworks.
2026
Winner — Code Innovation Series Hackathon
Hosted by IncubateIND in partnership with GitHub. Recognized for original, well-engineered tooling under competitive deadline.
2024 – Present
Founder & Lead Mentor — CyberSec Cohort
Independent mentorship program. Leading security research squads and teaching ethical hacking across India.
2025
Nullcon Berlin CTF — Competitor
Advanced Capture The Flag challenges. Real-world security analysis in a competitive environment.
2024 – Present
Independent Security Researcher
Active on multiple bug bounty platforms. Discovered and responsibly disclosed vulnerabilities.
2024 – Present
Open-Source Security Tool Developer
Maintaining ARMAGEDDON, DEMON PDF Crack Engine, PHOENIX OSINT Engine, Project Nexus, GhostRoute and WebRTC C2.
04 — Deployments

Case Files

Ref. DD—OPS—2026
CASE NO. 001 Research
Armageddon
Browser security research platform for analysing system behaviour under extreme resource conditions. Sixteen simultaneous test vectors, built for responsible disclosure and hardening — not for harm.
16Vectors
50WebGL Ctx
~500KBPayload
3–7sResponse
WebGL 2.0WASMGPU Analysis
CASE NO. 002 Tool
Demon PDF Crack v3.0
Professional PDF security recovery tool for authorized password recovery and security auditing. Five analysis methods, full Unicode support, GPU acceleration.
PythonAES-256GPU Accel
CASE NO. 003 Operational
Phoenix OSINT Engine
Flask-based OSINT platform correlating multiple intelligence sources — LeakOSINT, HIBP, Gravatar, DeHashed and social profile scraping — across email, phone and general intel query modes.
FlaskOSINTData Correlation
CASE NO. 004 Operational
Cyberwar // Banking Defense
Full-stack defensive platform modelling threat response for banking infrastructure. Django backend, React frontend — built for resilience under simulated attack conditions.
DjangoReactThreat Defense
C2 Sim

GHOSTROUTE

Encrypted command & control simulation framework for red team training environments, with modular payload delivery over secure channels.

Repository
P2P

WEBRTC C2

Browser-based peer-to-peer security research platform demonstrating secure P2P channels using the WebRTC protocol.

Repository
Auth

FORTRESS AUTH

Secure login web application with bcrypt/Argon2 hashing, SQL-injection protection and optional two-factor authentication.

Repository
ML

PHISHING ML DETECTOR

Scikit-learn classification model trained to identify phishing emails with a high detection accuracy rate.

Repository
Recon

VULNERABILITY SCANNER

Automated security assessment tool for open ports and weak configurations, with VAPT-ready reporting output.

Repository
05 — Credentials

Clearance Ledger

Ref. DD—CRD—2026

Ethical Hacker

Cisco
2026

Online Fraud Prevention

Hack & Fix
2026

Cybersecurity Job Simulation

Forage
2026

IAM Job Simulation

Forage
2026

Data Analytics Simulation

Deloitte / Forage
2026

Android Bug Bounty

EC-Council
2025

Intro to Cybersecurity

Cisco
2025

Cloud Computing

EC-Council
2025

SQLMap Certification

EC-Council
2025

Network Defense Essentials

EC-Council
2025

Ethical Hacking Essentials

EC-Council
2025

JavaScript Certification

IBM
2024

Cybersecurity Skilling

NSDC
2026
06 — Debrief

Frequently Asked

Ref. DD—FAQ—2026
A Cybersecurity Researcher, Ethical Hacker and Security Tool Developer from Kolkata. Creator of ARMAGEDDON, DEMON PDF Crack Engine, PHOENIX OSINT Engine, GhostRoute C2 and WebRTC C2. Currently completing a BSc in Cybersecurity at IAER Salt Lake.
A browser security research platform with sixteen test vectors for analysing system behaviour under resource load — built to surface browser vulnerabilities for responsible disclosure, not exploitation.
Yes — open to bug bounty collaborations, authorized red team engagements and security research. Reach out at dasj33561@gmail.com.
07 — Secure Channel

Establish Contact

Let's build something secure.

Open for bug bounty collaborations, authorized red team engagements and security research.